Swati KhandelwalNov 10, 2026Vulnerability / Cloud Security
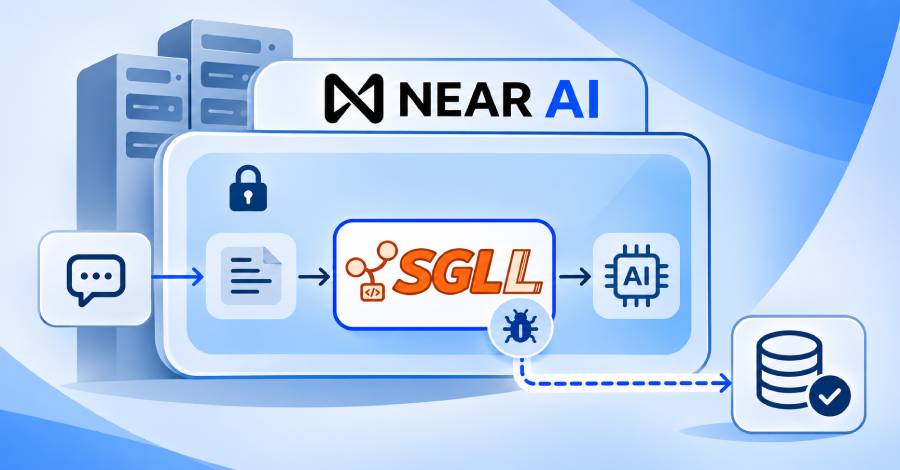
An attacker exploited a remote code execution flaw in SGLang, an open-source inference engine, and ran code on one of NEAR AI's inference servers last Sunday.
The attacker could also have seen requests being processed on that server that day, including requests sent in confidential mode, the company said earlier this week. That mode processes requests inside a trusted execution environment (TEE) designed to keep them private even from the company itself.
But the TEE "does not protect against a vulnerability in the software running inside the environment," the company said. SGLang runs inside the TEE, which is how the attacker could reach requests there.
That access has since been closed, but not before the attacker moved further into the company's systems.
The attacker reached an internal system behind Private Chat, a product the company had already deprecated. So far, the company has confirmed that the attacker downloaded account details for about 100 users there. These are email addresses and names, and for some accounts, plan and balance information.